Skip to content
Artwork for Security Breach
NewsTech NewsTechnologyBusiness News

Security Breach

Eric Sorensen

A weekly discussion of new developments and the latest cybersecurity threats, including ransomware, malware, phishing schemes, DDoS attacks and more, facing the U.S. industrial sector.

Play
  • 23 episodes
  • fortnightly
  • Avg 35 min
  • English
Counted on this page — what you have heard stays on this device, so it is not something the list can be paged by.
  • Dec 4, 2025 · 46 min

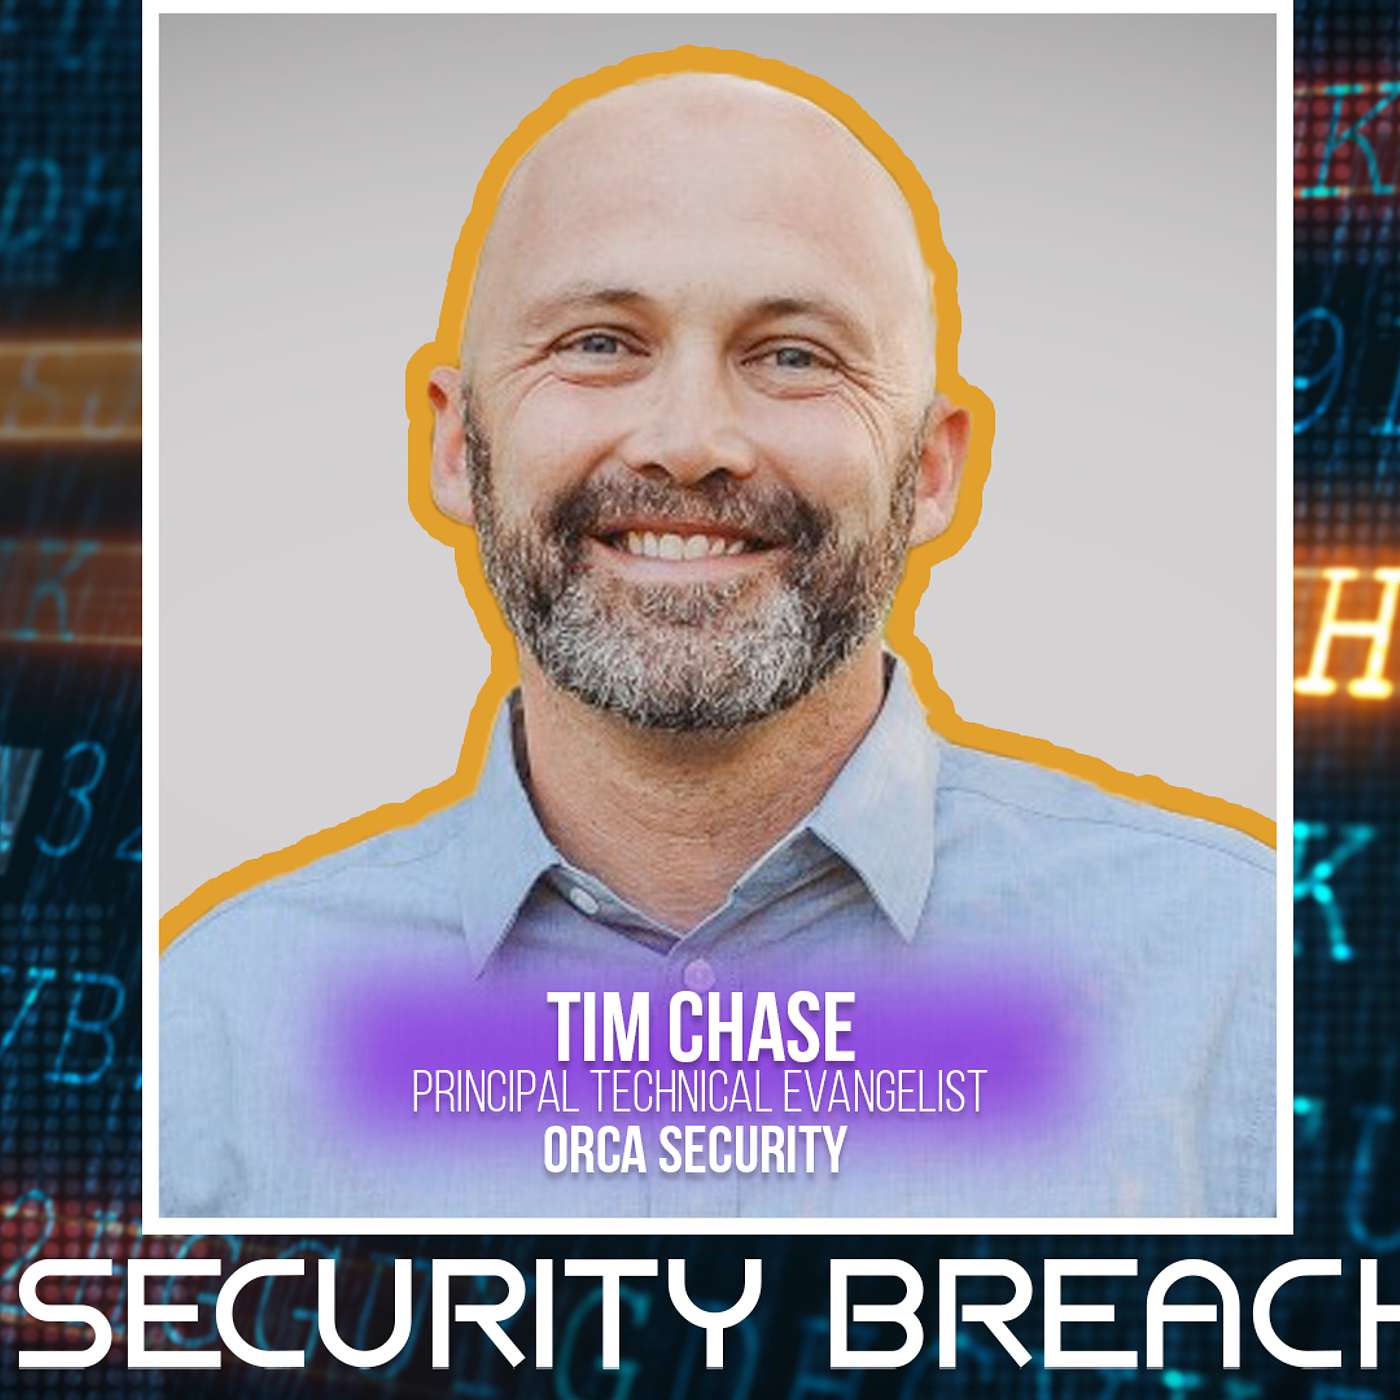
    Speaking the Right Language

    Send us Fan Mail Perhaps you’re familiar with the quote, “The greatest trick the Devil ever pulled was convincing the world he didn’t exist.” While its use in the movie The Usual Suspects might resonate with most, the original attribution goes to French poet Charles Baudelaire. The quote came to mind in preparing for my conversation with Tim Chase, Principal Technical Evangelist for Orca Security. I knew we were going to be discussing topics where the biggest implementation challenges typically resonate from OT asset owners who don’t see the need to address these topics. Or, with all due respect to Baudelaire, the greatest trick hackers ever pulled was convincing the industrial sector that they didn’t care. The good news is that folks like Tim are aware of these situations, and working to offer some new solutions. Watch/listen as we discuss: How vital it is to define security responsibilities. The growing need for cloud security education. Why a top-down approach is vital for creating a security-focused culture. The benefits of creating internal security champions. The annoying, but growing significance of SBOMs. Combatting alert fatigue. The biggest challenges AI is creating for cybersecurity. As a go-to podcast for our listeners, we want to help you align your brand with our expertise. By sponsoring our podcast, your brand will build trust, and your message will stand out to an audience searching for tools to assist their cybersecurity efforts. Click Here to Become a Sponsor. To catch up on past episodes, you can go to Manufacturing.net, IEN.com or MBTmag.com. You can also check Security Breach out wherever you get your podcasts, including Apple, Amazon and Overcast. If you have a cybersecurity story or topic that you’d like to have us explore on Security Breach, you can reach me at jeff@ien.com.

  • Nov 14, 2025 · 49 min

    Why People Are Not the Biggest Risk

    Send us Fan Mail While I’ll resist drawing comparisons about industrial cybersecurity to butterflies and bees, producing this episode did remind me of another great Muhammad Ali quote: "The hands can't hit what the eyes can't see.” This could provide an easy segue into the ongoing challenges about asset visibility, but really, it goes a bit deeper than that. In addition to being able to see all the things we need to defend against, we also have to understand what to look for in establishing those defenses. In this episode, we discuss these challenges and solutions with Bryson Bort, the founder and CEO of SCYTHE, a leading provider of Adversarial Exposure Validation (AEV) solutions. Watch/listen as we also discuss: The increasing impact of hacktivists. The rise of ransomware gangs. What AEV is all about. Why there is no such thing as an accidental hack. The human impact on cybersecurity and why it is rarely the human's fault. How his former military life has impacted his cybersecurity career. Why supply chains could be the most important threat landscape going forward. To check out the work he and his colleagues are up to, you can go to scythe.io, as well as icsvillage.com. As a go-to podcast for our listeners, we want to help you align your brand with our expertise. By sponsoring our podcast, your brand will build trust, and your message will stand out to an audience searching for tools to assist their cybersecurity efforts. Click Here to Become a Sponsor. To catch up on past episodes, you can go to Manufacturing.net, IEN.com or MBTmag.com. You can also check Security Breach out wherever you get your podcasts, including Apple, Amazon and Overcast. If you have a cybersecurity story or topic that you’d like to have us explore on Security Breach, you can reach me at jeff@ien.com.

  • Oct 31, 2025 · 31 min

    Preserving Uptime in the Face of Evolving Attacks

    Send us Fan Mail Uptime. It’s the lifeblood of manufacturing and the precise target of industrial sector hackers. By knocking systems offline, stealing credentials, holding data for ransom, or crippling supply chains, the bad guys know their ultimate goals of disruption or extortion will be realized. And as we’ve discussed numerous times here on Security Breach, keeping these bad actors out has become more and more difficult as new technology, connectivity and endpoints are added to the OT landscape. Hackers are getting smarter and more complex, but the good news is so are the tools and strategies for the good guys. Here to offer some perspective on dealing with the leading threats targeting the people, systems and data of the industrial sector is a collection of experts focused on minimizing disruptions and preparing you to react and respond to cyberattacks. Watch/listen as: Max Clausen, senior VP of Network Connectivity at Zayo dives into the factors and strategies driving DDoS or distributed denial of service attacks. John Carse, Field CISO at SquareX discusses the ongoing impact of developing and legacy vulnerabilities, as well as some of the novel strategies hackers are using to introduce new strands of highly disruptive malware. Amit Hammer, CEO of Salvador Tech talks about lessons learned from the recent Jaguar Land Rover attack and how response strategies will continue to play a key role in minimizing attack-related downtime. As a go-to podcast for our listeners, we want to help you align your brand with our expertise. By sponsoring our podcast, your brand will build trust, and your message will stand out to an audience searching for tools to assist their cybersecurity efforts. Click Here to Become a Sponsor. To catch up on past episodes, you can go to Manufacturing.net, IEN.com or MBTmag.com. You can also check Security Breach out wherever you get your podcasts, including Apple, Amazon and Overcast. If you have a cybersecurity story or topic that you’d like to have us explore on Security Breach, you can reach me at jeff@ien.com.

Showing 21–23 of 23 episodes