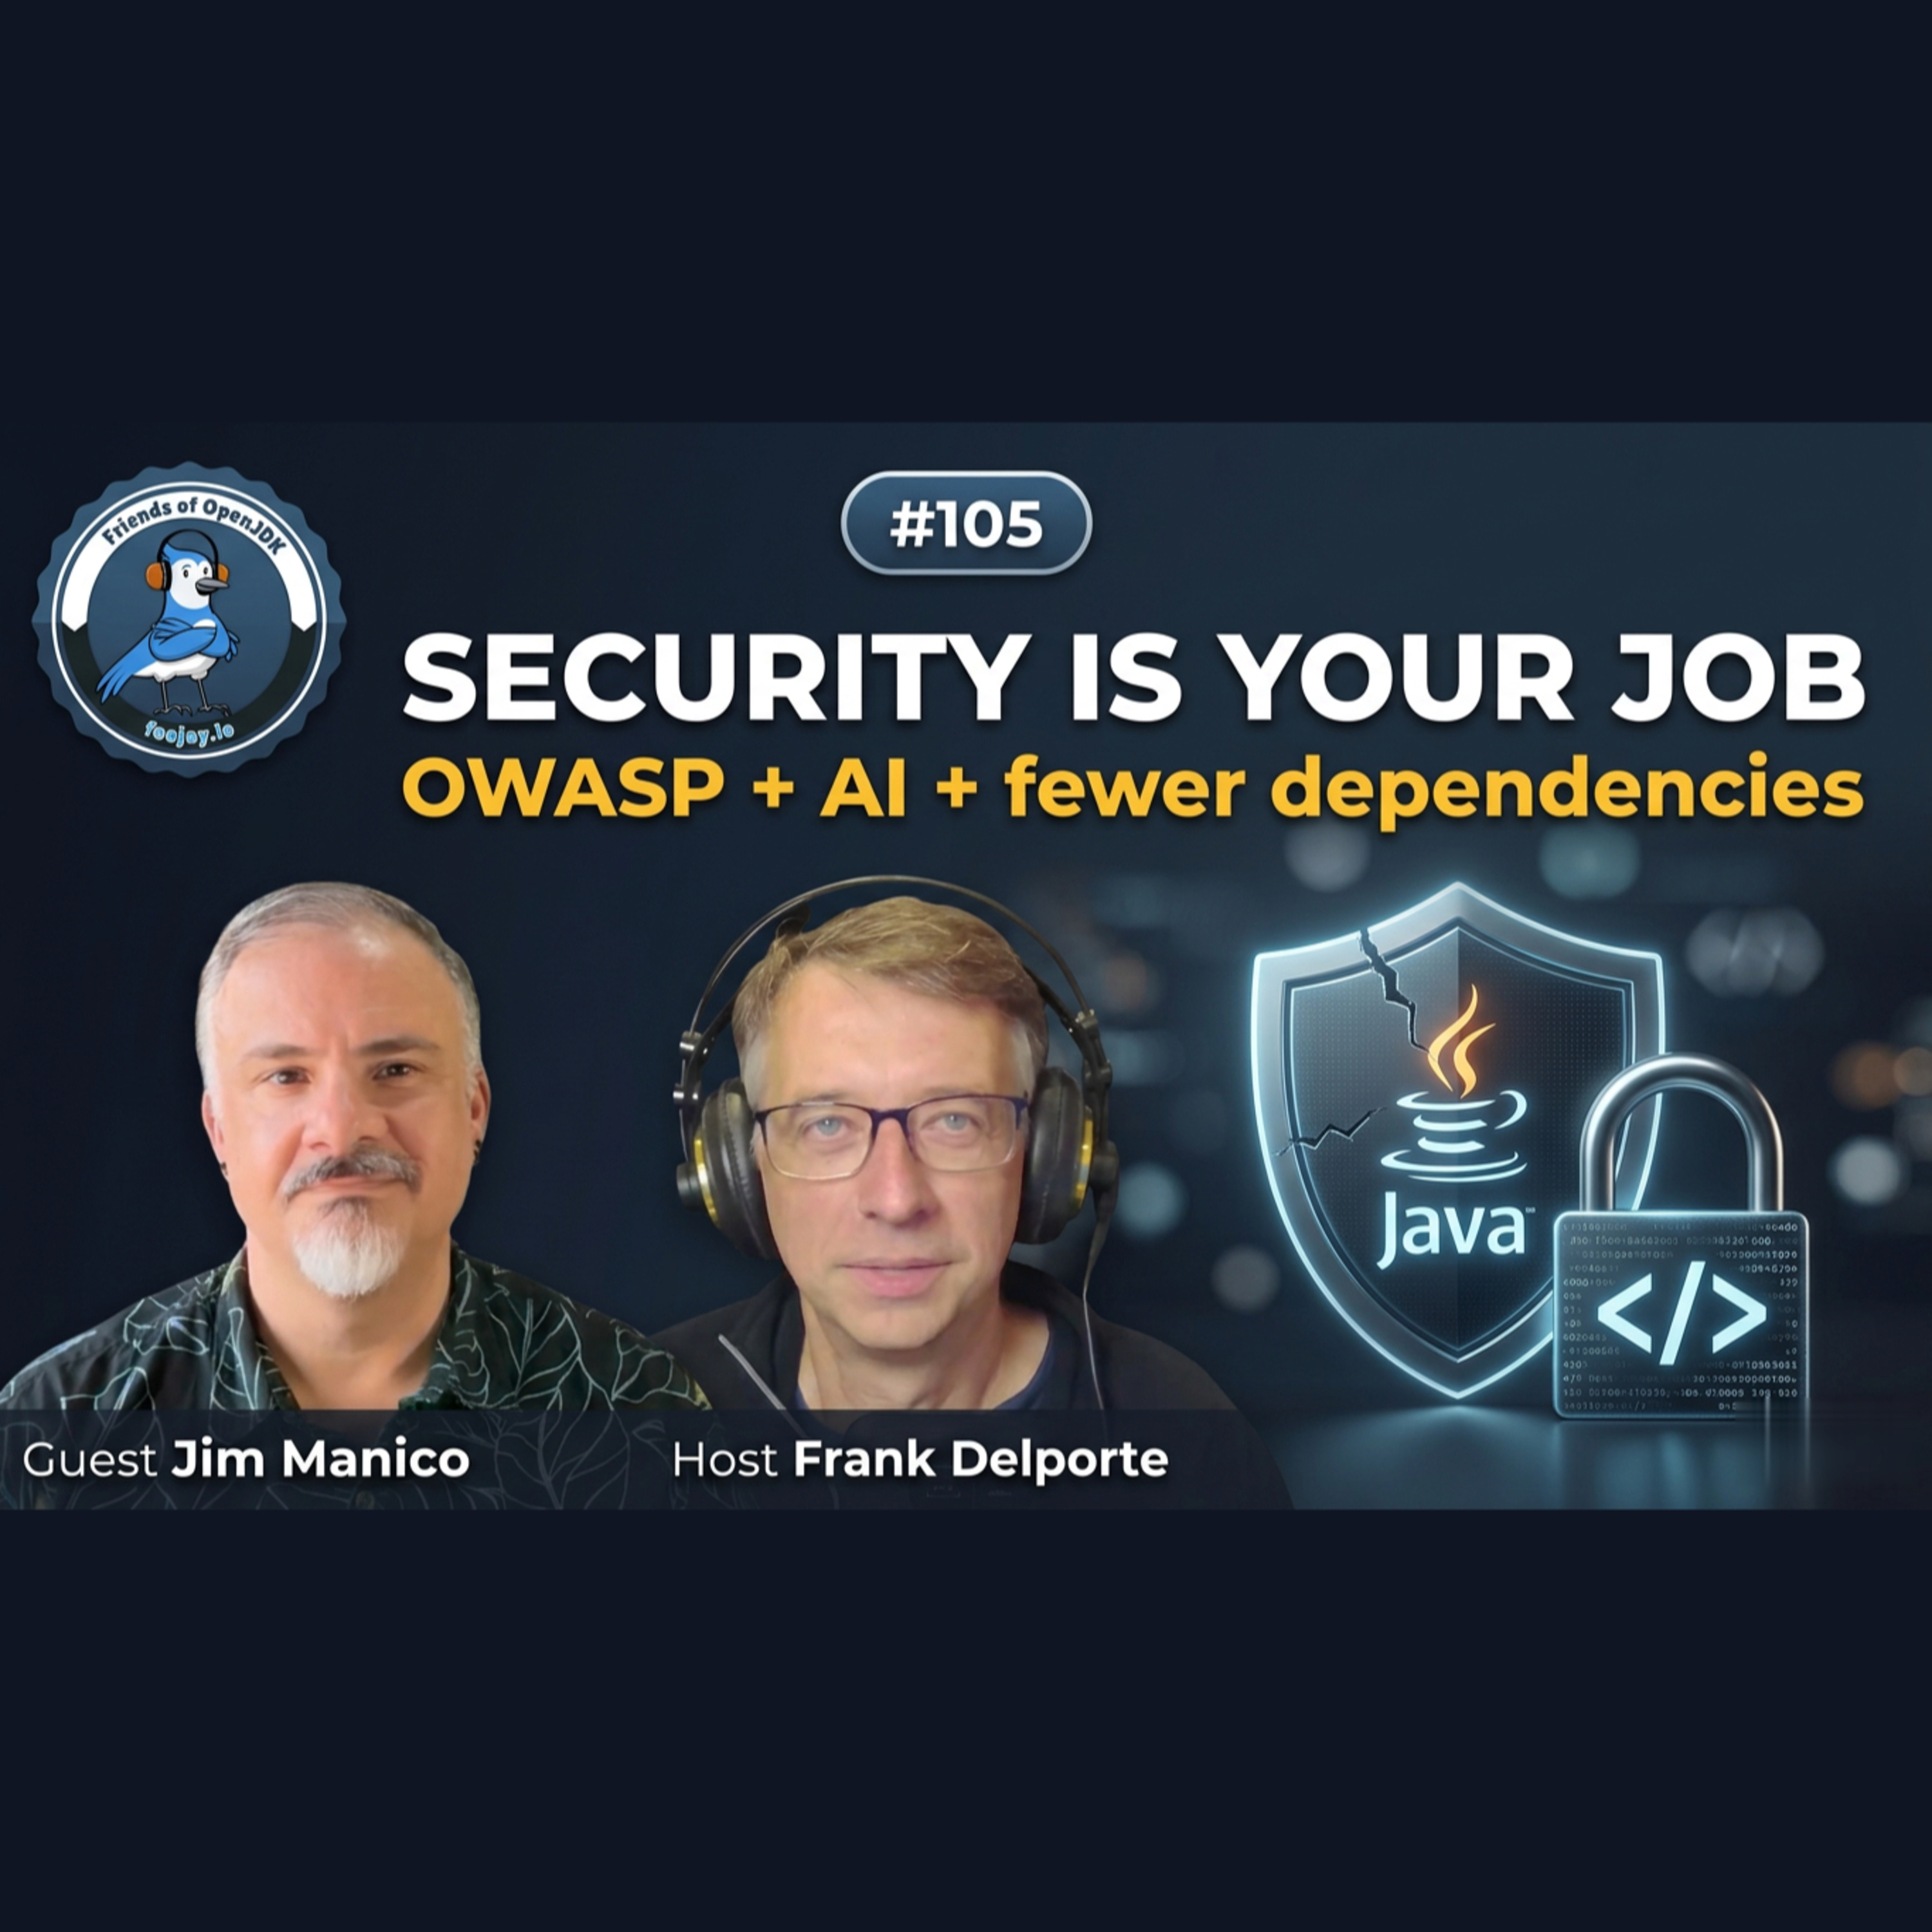
Security Is Your Job: OWASP, AI and Safer Java Dependencies with Jim Manico (Foojay Podcast #105)
How safe is your Java application, and how safe are the dependencies it ships with? If you build software that handles sensitive data and you have no security process, OWASP's Jim Manico has a blunt word for it: negligent. In this episode, Jim Manico, founder of Manicode Security, Java Champion and OWASP project leader, explains what OWASP is and which of its projects matter to Java developers. He brought the OWASP Java Encoder, Java HTML Sanitizer and JSON Sanitizer back to life with AI-assisted workflows, and tells us what he learned along the way. Topics include: When to use the OWASP Java Encoder versus the Java HTML Sanitizer Why untrusted input must be checked on both the client and the server How a few kilobytes of nested CSS can cause a denial-of-service Why chained small vulnerabilities become a major one in the age of AI Why Jim wants far fewer third-party libraries, and how to keep the rest up to date What to do first when your team has no security process Guest: Jim Manico Founder of Manicode Security, Java Champion and OWASP project leader Jim on LinkedIn Links: Full show notes with all links OWASP Java Security Libraries: Please Update OWASP Java Encoder OWASP Java HTML Sanitizer trim-reaper on GitHub Timestamps: 00:00 Introduction of topic and guest 02:11 What is OWASP? 04:10 How AI influences the speed of OWASP changes. Who contributes. 06:30 Which OWASP projects you should know as a Java developer 07:30 How Jim uses AI to evolve his libraries 08:28 When to use OWASP Java Encoder and OWASP Java HTML Sanitizer 13:58 User input needs to be checked in all steps (UI and backend) 16:07 Man-in-the-middle attacks (eMuhdra) 17:17 How to keep your systems up-to-date + minimize your dependencies 22:34 How CSS can cause a denial-of-service problem 24:52 How multiple small security issues can be combined into a major issue 26:36 How to handle the growing number of discovered vulnerabilities 29:13 The era of coding is coming to an end but you can still be a master developer 32:45 How to automate upgrading with Maven, Gradle, and other tools 36:42 What Java developers can learn from recent security problems (like PHP and eMuhdra) 38:42 You must have a security process! Make your managers aware... 43:53 How to get involved in OWASP 46:08 What to remember from this podcast: security is your responsibility!