Skip to content
Artwork for David Bombal

David Bombal

David Bombal

David Bombal interviews people in the networking world to learn about life, hacks, technology and networking and ways to improve your life!

Play
  • 42 episodes
  • Avg 31 min
  • English
Counted on this page — what you have heard stays on this device, so it is not something the list can be paged by.
  • S1 · E1
    Monday · 25 min

    #620: He Invented the USB Rubber Ducky to Fix Printers!

    Big thanks to Proton VPN for sponsoring this video. To get a 75% discount on Proton VPN this Black Friday month, please use the following link: https://protonvpn.com/davidbombal // Buy Hak5 coolness // Buy Hak5 stuff here: https://davidbombal.wiki/gethak5 Why does the USB Rubber Ducky look like a normal flash drive but behave like a keyboard? Darren Kitchen, founder of ‪@hak5‬, tells David Bombal how a tool for fixing printers became a famous hacking device. ‪@DarrenKitchen‬ shares the story behind the USB Rubber Ducky, from hiding early circuit boards inside actual rubber ducks to building DuckyScript and developing a security tool used for automation, awareness training, and authorized red teaming. We explore why computers accept input from USB keyboards, how keystroke injection works, and why an apparently harmless device can issue commands much faster than a person. Darren also explains Keystroke Reflection, a technique that uses keyboard indicator signals such as Caps Lock, Num Lock, and Scroll Lock to transfer small amounts of data without relying on a normal network connection, when the host and access conditions permit it. In this conversation: • Why the Rubber Ducky originally helped Darren fix printers and network shares • How a USB device can identify itself as a human interface device (HID) • What DuckyScript does and how it evolved • The security implications of high-speed keystroke injection • How Keystroke Reflection works in principle, including air-gapped scenarios • Darren's stories about the Rubber Ducky appearing in television and film Learn more about the USB Rubber Ducky: https://shop.hak5.org/products/usb-ru... Hak5's explanation of Keystroke Reflection: https://shop.hak5.org/blogs/usb-rubbe... What surprised you most: that it started as an IT shortcut, or the keyboard LED technique? Let us know in the comments. This interview discusses security research and authorized testing. Only use security tools on systems you own or are explicitly permitted to assess. // Darren Kitchen SOCIAL // YouTube: / darrenkitchen Website: https://hak5.org/pages/hack-across-am... X: https://x.com/hak5darren // Hak5 WEBSITE // https://davidbombal.wiki/gethak5 // David's SOCIAL // Discord: discord.com/invite/usKSyzb Twitter: www.twitter.com/davidbombal Instagram: www.instagram.com/davidbombal LinkedIn: www.linkedin.com/in/davidbombal Facebook: www.facebook.com/davidbombal.co TikTok: tiktok.com/@davidbombal YouTube: / @davidbombal Spotify: open.spotify.com/show/3f6k6gE... SoundCloud: / davidbombal Apple Podcast: podcasts.apple.com/us/podcast... // MY STUFF // https://www.amazon.com/shop/davidbombal // SPONSORS // Interested in sponsoring my videos? Reach out to my team here: sponsors@davidbombal.com Please note that links listed may be affiliate links and provide me with a small percentage/kickback should you use them to purchase any of the items listed or recommended. Thank you for supporting me and this channel! Disclaimer: This video is for educational purposes only. #USBRubberDucky #Hak5 #Cybersecurity
  • S1 · E1
    Monday · 8 min

    #619: This Doom Game Deletes Real Kubernetes Pods

    Big thanks to Cisco & Splunk for sponsoring my trip to .Conf 2026 and also for sponsoring this video. What happens when shooting an enemy in a Doom game deletes a real Kubernetes pod? Splunk built a Doom clone that does exactly that, then tracks the chaos in live dashboards. In this video, Heath shows me Metric Mayhem, a Doom-style game connected to a live e-commerce demo application running on Kubernetes. Enemies represent pods in the application, so playing the game creates real failures for Splunk to monitor. We also look at Trace Invaders, Splunk’s take on Space Invaders, and how Chaos Mesh adds CPU stress, memory stress, and latency to the environment. Heath explains how the team captures game events as logs and turns them into dashboards showing deleted pods, player scores, boss defeats, and finish times. In this video: How game enemies map to Kubernetes pods What happens in the demo when a pod is deleted and replaced How Chaos Mesh introduces stress and latency How Splunk Observability Cloud shows the impact on the application How game logs power Splunk dashboards and leaderboards Why an interactive game makes a monitoring demo easier to understand If you’re learning Kubernetes, chaos engineering, or observability, this is a fun way to see how failures become useful data. Would you try this in your own test lab? Let me know in the comments. // Heath Johnson SOCIAL // LinkedIn: / heathjohnsonvm // David's SOCIAL // Discord: discord.com/invite/usKSyzb Twitter: www.twitter.com/davidbombal Instagram: www.instagram.com/davidbombal LinkedIn: www.linkedin.com/in/davidbombal Facebook: www.facebook.com/davidbombal.co TikTok: tiktok.com/@davidbombal YouTube: / @davidbombal Spotify: open.spotify.com/show/3f6k6gE... SoundCloud: / davidbombal Apple Podcast: podcasts.apple.com/us/podcast... // MY STUFF // https://www.amazon.com/shop/davidbombal // SPONSORS // Interested in sponsoring my videos? Reach out to my team here: sponsors@davidbombal.com Please note that links listed may be affiliate links and provide me with a small percentage/kickback should you use them to purchase any of the items listed or recommended. Thank you for supporting me and this channel! Disclaimer: This video is for educational purposes only. #SplunkSponsored #Kubernetes #SplunkConf

  • S1 · E1
    November 4 · 34 min

    #618: Your Smart Device Is Tracking You More Than You Think

    Big thanks to Proton Drive for sponsoring this video. You can use my link proton.me/drive/davidbombal to sign up for Proton Drive and get 40% discount. // Glen Sorensen’s SOCIAL // LinkedIn: / glen-sorensen DeleteMe LinkedIn: / deleteme // Article REFERENCE // protonvpn.com/blog/windows-is... // David's SOCIAL // Discord: discord.com/invite/usKSyzb Twitter: www.twitter.com/davidbombal Instagram: www.instagram.com/davidbombal LinkedIn: www.linkedin.com/in/davidbombal Facebook: www.facebook.com/davidbombal.co TikTok: tiktok.com/@davidbombal YouTube: / @davidbombal Spotify: open.spotify.com/show/3f6k6gE... SoundCloud: / davidbombal Apple Podcast: podcasts.apple.com/us/podcast... // MY STUFF // www.amazon.com/shop/davidbombal // SPONSORS // Interested in sponsoring my videos? Reach out to my team here: sponsors@davidbombal.com Please note that links listed may be affiliate links and provide me with a small percentage/kickback should you use them to purchase any of the items listed or recommended. Thank you for supporting me and this channel! Disclaimer: This video is for educational purposes only. #privacy #vpn #internet

  • S1 · E1
    November 4 · 42 min

    #617: This Is How NVIDIA's AI Mercedes Drives in Real Traffic

    What happens when NVIDIA's AI drives a Mercedes-Benz CLA through Berlin traffic? David Bombal rides along to see how Alpamayo and the Halos safety stack work together. At GTC Berlin, I ride in a Mercedes-Benz CLA running a development version of NVIDIA's Alpamayo driving software. We encounter cyclists, pedestrians, narrow roads, unusual junctions, parked cars and unpredictable drivers while the car handles much of the driving under human supervision. We look at what is actually happening behind the scenes: an end-to-end AI model proposes a driving path, a separate classical safety stack checks the environment and rules, and a trajectory arbiter decides when to allow the plan or fall back. The car uses on-board NVIDIA DRIVE Orin computing, cameras, radar and ultrasonic sensors. We also discuss training with US and European driving data, simulation with NVIDIA Cosmos, the difference between this development vehicle and NVIDIA's downloadable Alpamayo research models, and what it takes to adapt the system to different vehicles and countries. In this video: • A live AI-assisted drive through busy Berlin streets • How Alpamayo and the classical Halos safety stack work together • Why narrow roads, cyclists and German traffic lights are difficult cases • The cameras, radar, ultrasonic sensors and DRIVE Orin hardware • How real-world data and Cosmos simulation help train and test driving models • Which Alpamayo research models you can explore yourself Important: this demonstration is a supervised Level 2 driver-assistance system. The person in the driver's seat remains attentive and responsible; this is not an unsupervised robotaxi. Would you trust AI-assisted driving in a busy city? Which situation would you want it to handle first? NVIDIA Alpamayo: https://www.nvidia.com/en-us/solution... NVIDIA Halos: https://www.nvidia.com/en-us/ai-trust... Alpamayo research downloads: https://developer.nvidia.com/drive/do... Discord: discord.com/invite/usKSyzb Twitter: www.twitter.com/davidbombal Instagram: www.instagram.com/davidbombal LinkedIn: www.linkedin.com/in/davidbombal Facebook: www.facebook.com/davidbombal.co TikTok: tiktok.com/@davidbombal YouTube: / @davidbombal Spotify: open.spotify.com/show/3f6k6gE... SoundCloud: / davidbombal Apple Podcast: podcasts.apple.com/us/podcast... // TIMESTAMPS // 0:00 - Intro 0:39 - Not a normal Mercedes 01:42 - How the Alpamayo stack works 02:52 - Levels of self-driving cars 04:01 - How the cameras work 05:10 - Difference between Alpamayo and Halos 07:49 - Self-driving cars in the future 08:30 - Alpamayo vs standard LLM 10:00 - Going for a drive // Training the AI model 14:52 - Alpamayo and Halos working together 15:38 - Left side and right side driving 16:21 - Smooth driving behaviour 18:47 - Petrol (Gas) vs electric cars 19:47 - Real-world scenario driving 21:16 - Petrol (Gas) vs electric cars continued 22:56 - Unique traffic laws 25:49 - The future of Aplamayo and Halos 26:49 - Difference to other self-driving cars 28:45 - Aplamayo on Hugging Face 30:35 - Trusting self-driving cars 33:02 - Handling unusual scenarios 34:17 - Adjusting acceleration based on the vehicle 37:05 - Hardware explained 38:43 - Self-driving cars in the future pt.2 39:57 - How the model is trained 41:38 - Conclusion #NVIDIA #AutonomousDriving #Alpamayo

  • S1 · E1
    October 26 · 19 min

    #616: How Police Can Track Your Phone

    Big thanks to ThreatLocker for sponsoring my trip to Black Hat USA 2026 and also for sponsoring this video. To start your free trial with ThreatLocker please use the following link: https://www.threatlocker.com/davidbombal Your phone can be tricked into connecting to a fake cell tower. These devices are commonly known as Stingrays, cell-site simulators or IMSI catchers. They can be used to identify and locate phones in an area, and some attacks can interfere with the security of your cellular connection. At Black Hat and DEF CON, I spoke to Cooper Quintin, Senior Staff Technologist at the Electronic Frontier Foundation (EFF), about Rayhunter. Rayhunter is an open-source project from the EFF designed to detect suspicious cellular activity using inexpensive mobile hotspot hardware. In this interview, Cooper explains how Stingrays and IMSI catchers work, why your phone can connect to a fake cell tower, what an IMSI is, how cellular downgrade attacks work, what a null cipher is, how Rayhunter detects suspicious activity, and what the EFF has learned from real-world deployments. We also get into mobile forensic extraction, phone searches at the border, biometrics vs PINs and passwords, and the bigger question of how much surveillance power governments and law enforcement should have. Thanks to ThreatLocker for sponsoring my trip to Black Hat and DEF CON and for sponsoring this video. #CyberSecurity #Privacy #Hacking // Cooper Quintin’s SOCIAL // EFF Website: https://www.eff.org/about/staff/coope... LinkedIn: / cooper-quintin-932029125 Website: https://cooperq.com/ // Web Page REFERENCE // https://www.eff.org/deeplinks/2025/03... https://www.eff.org/ https://ssd.eff.org/ // David's SOCIAL // Discord: discord.com/invite/usKSyzb Twitter: www.twitter.com/davidbombal Instagram: www.instagram.com/davidbombal LinkedIn: www.linkedin.com/in/davidbombal Facebook: www.facebook.com/davidbombal.co TikTok: tiktok.com/@davidbombal YouTube: / @davidbombal Spotify: open.spotify.com/show/3f6k6gE... SoundCloud: / davidbombal Apple Podcast: podcasts.apple.com/us/podcast... // MY STUFF // https://www.amazon.com/shop/davidbombal // SPONSORS // Interested in sponsoring my videos? Reach out to my team here: sponsors@davidbombal.com Please note that links listed may be affiliate links and provide me with a small percentage/kickback should you use them to purchase any of the items listed or recommended. Thank you for supporting me and this channel! Disclaimer: This video is for educational purposes only. #cybersecurity #bhusa26 #privacy

  • October 20 · 15 min

    #615: How is AI Changing Cybersecurity?

    Big thanks to Cisco & Splunk for sponsoring my trip to .Conf 2026 and also for sponsoring this video. // Kamal Hathi’s’ SOCIAL // LinkedIn: / kamal-hathi // Hanlin Fang’s SOCIAL // LinkedIn: / hanlinfang // Jessica Oppenheimer’s SOCIAL // LinkedIn: / jessbair // Craig Woolley’s SOCIAL // LinkedIn: / craig-woolley-783059111 // Tom Smit’s SOCIAL // LinkedIn: / tsmit50 // Bruce Snell’s SOCIAL // LinkedIn: / brucesnell-security // Heath Johnson’s SOCIAL // LinkedIn: / heathjohnsonvm // Paul Bannister’s SOCIAL // LinkedIn: / paul-bannister // Hao Yang’s SOCIAL // LinkedIn: / hao-yang-bb6ab429 // Robert Castley’s SOCIAL // LinkedIn: / robertcastley // Leila Reyhani’s SOCIAL // LinkedIn: / leila-reyhani // David's SOCIAL // Discord: discord.com/invite/usKSyzb Twitter: www.twitter.com/davidbombal Instagram: www.instagram.com/davidbombal LinkedIn: www.linkedin.com/in/davidbombal Facebook: www.facebook.com/davidbombal.co TikTok: tiktok.com/@davidbombal YouTube: / @davidbombal Spotify: open.spotify.com/show/3f6k6gE... SoundCloud: / davidbombal Apple Podcast: podcasts.apple.com/us/podcast... // MY STUFF // https://www.amazon.com/shop/davidbombal // SPONSORS // Interested in sponsoring my videos? Reach out to my team here: sponsors@davidbombal.com Please note that links listed may be affiliate links and provide me with a small percentage/kickback should you use them to purchase any of the items listed or recommended. Thank you for supporting me and this channel! Disclaimer: This video is for educational purposes only. #splunk #cybersecurity #ai

  • S1 · E1
    October 20 · 43 min

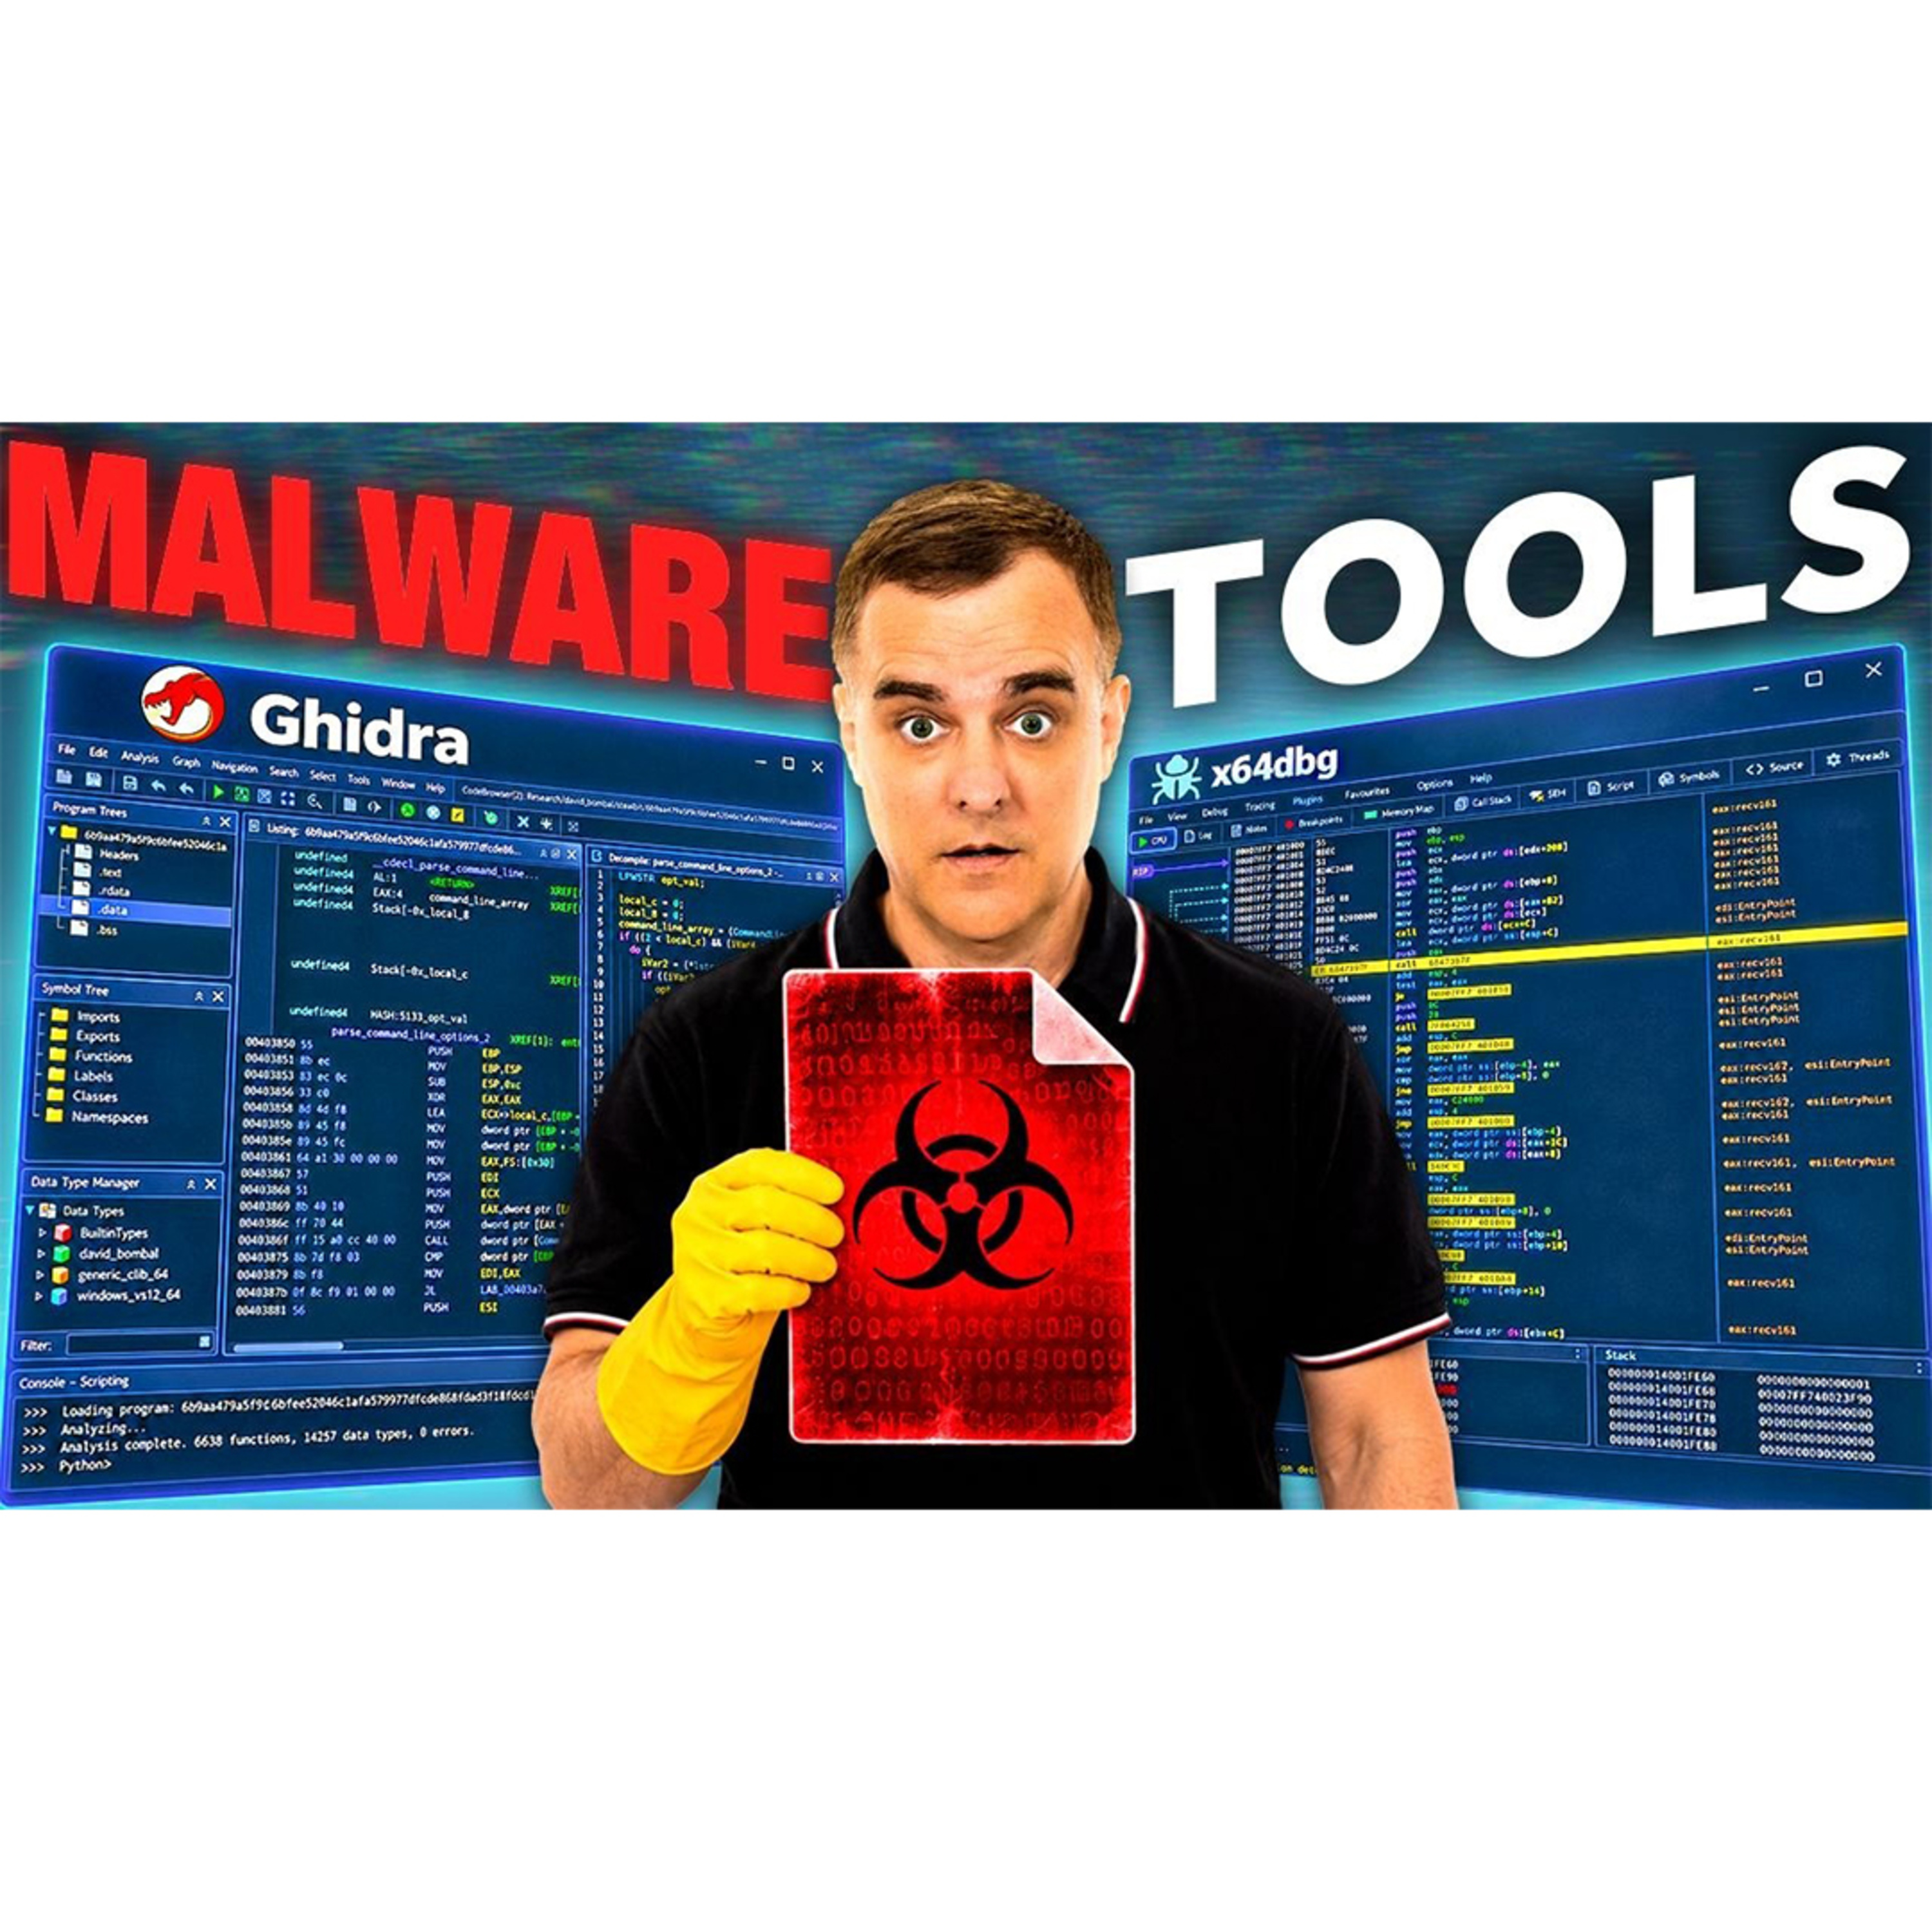
    #614: Learn Malware Analysis with Ghidra and x64dbg (for free)

    Want to learn how to reverse engineer malware? Lindsay Kaye joins me to demonstrate malware analysis using Ghidra and x64dbg, two free tools you can use to develop your skills. Lindsay is the author of Dissecting the Dark Web. In this interview, we take apart a data theft tool used by LockBit affiliates and examine BlackMatter ransomware. You’ll see how malware detects a debugger, hides strings, and loads functions at runtime. We also run ransomware in a lab VM to show what happens to the victim’s files. We discuss: • How ransomware gangs steal data before encrypting it • How static and dynamic analysis work together • Finding malware indicators in Sysmon logs • Why ransomware can print physical ransom notes • How reputation and trust work in criminal forums • How to start reverse engineering by compiling your own C programs and examining them in Ghidra If you have some programming knowledge and want to understand how malware works, this is a practical look at the skills involved. // Sponsored SEGMENT // Big thank you to Proton Pass for sponsoring this video. To sign up for Proton Pass, please use the following link https://proton.me/davidbombal to get Proton Pass free. // Link to No Starch Website for Lindsay Kaye’s Book // Order Dissecting the Dark Web on No Starch: https://nostarch.com/dissecting-the-d... Use Coupon Code KAYE25 for 25% off Dissecting the Dark Web at NoStarch.com // Lindsay Kaye’s SOCIALS // Website: https://www.lindsaymkaye.com/ LinkedIn: / lindsaymkaye Human Security Website: https://www.humansecurity.com/people/... // David's SOCIAL // Discord: discord.com/invite/usKSyzb Twitter: www.twitter.com/davidbombal Instagram: www.instagram.com/davidbombal LinkedIn: www.linkedin.com/in/davidbombal Facebook: www.facebook.com/davidbombal.co TikTok: tiktok.com/@davidbombal YouTube: / @davidbombal Spotify: open.spotify.com/show/3f6k6gE... SoundCloud: / davidbombal Apple Podcast: podcasts.apple.com/us/podcast... // MY STUFF // https://www.amazon.com/shop/davidbombal // SPONSORS // Interested in sponsoring my videos? Reach out to my team here: sponsors@davidbombal.com Please note that links listed may be affiliate links and provide me with a small percentage/kickback should you use them to purchase any of the items listed or recommended. Thank you for supporting me and this channel! Disclaimer: This video is for educational purposes only. #defcon #reverseengineering #darkweb

  • S1 · E1
    October 12 · 27 min

    #613: Think You’re Private Online? Watch This

    Big thank you to DeleteMe for sponsoring this video. Use my link join https://joindeleteme.com/Bombal or use the QR code in the video to get 20% off. How private are the apps you use every day? I sit down with Thorin Klosowski from the Electronic Frontier Foundation (EFF) to discuss online privacy, secure messaging, VPNs and the data we share with AI tools. We look at Signal, WhatsApp and Telegram, discuss privacy tradeoffs across Windows, Linux, Android and iPhone, and ask what you should assume about email and cloud storage. Thorin also walks through EFF’s free Surveillance Self-Defense guides to help you create a security plan and decide what to focus on first. If you work in cybersecurity, or you simply want to help your family protect their privacy, this conversation gives you a starting point without assuming everyone needs the same tools. In this interview: Why “I have nothing to hide” misses the point How to think about passwords, two-factor authentication and security planning Why messaging defaults and privacy settings matter What a VPN can and cannot do for your privacy AI features, cloud storage and questions to ask about your data Phone and computer privacy tradeoffs, email and encryption Which privacy setting or app are you going to review first? Let me know in the comments, and subscribe for more cybersecurity and privacy conversations. // Thorin Klosowski’s SOCIALS // Website: https://www.eff.org/about/staff/thori... EFF LinkedIn: https://www.linkedin.com/company/eff?... // Web page REFERENCE // https://ssd.eff.org/ // David's SOCIAL // Discord: discord.com/invite/usKSyzb Twitter: www.twitter.com/davidbombal Instagram: www.instagram.com/davidbombal LinkedIn: www.linkedin.com/in/davidbombal Facebook: www.facebook.com/davidbombal.co TikTok: tiktok.com/@davidbombal YouTube: / @davidbombal Spotify: open.spotify.com/show/3f6k6gE... SoundCloud: / davidbombal Apple Podcast: podcasts.apple.com/us/podcast... // MY STUFF // https://www.amazon.com/shop/davidbombal // SPONSORS // Interested in sponsoring my videos? Reach out to my team here: sponsors@davidbombal.com // MENU // 0:00 - Coming Up 0:40 – Intro & about the EFF 02:50 – DeleteMe Sponsored Section 05:08 – Surveillance & Self-Defence Tools 08:41 – Tool Guides, AI Privacy & Cloud Storage 13:29 – Messaging Apps to use 16:27 – Operating Systems to use 21:16 – How Secure is Email & Encryption 23:22 – Security Tips for Activists & Protestors 26:53 – Closing & Conclusion Please note that links listed may be affiliate links and provide me with a small percentage/kickback should you use them to purchase any of the items listed or recommended. Thank you for supporting me and this channel! Disclaimer: This video is for educational purposes only. #Privacy #CyberSecurity #EFF

  • October 8 · 18 min

    #612: How Hackers Trick AI Into Giving Up Secrets (Demos and free labs)

    Big thanks to Proton Drive for sponsoring this video. You can use my link http://proton.me/drive/davidbombal to sign up for Proton Drive and get 40% discount. // Free AI labs // Prompt Injection Taxonomy: https://arcanum-sec.github.io/arc_pi_... AI Security Resource Hub: https://arcanum-sec.github.io/ai-sec-... // Jason Haddix’s SOCIALS // X: https://x.com/Jhaddix?lang=en Github: https://github.com/Arcanum-Sec Website: https://arcanum-sec.com/ // David's SOCIAL // Discord: discord.com/invite/usKSyzb Twitter: www.twitter.com/davidbombal Instagram: www.instagram.com/davidbombal LinkedIn: www.linkedin.com/in/davidbombal Facebook: www.facebook.com/davidbombal.co TikTok: tiktok.com/@davidbombal YouTube: / @davidbombal Spotify: open.spotify.com/show/3f6k6gE... SoundCloud: / davidbombal Apple Podcast: podcasts.apple.com/us/podcast... // MY STUFF // https://www.amazon.com/shop/davidbombal // SPONSORS // Interested in sponsoring my videos? Reach out to my team here: sponsors@davidbombal.com Please note that links listed may be affiliate links and provide me with a small percentage/kickback should you use them to purchase any of the items listed or recommended. Thank you for supporting me and this channel! Disclaimer: This video is for educational purposes only. #ai #aihacking #promptinjection

  • S1 · E1
    October 1 · 22 min

    #611: Building AI Agents? Set Up These Guardrails First

    Big thanks to ‪@Cisco‬ & ‪@Splunkofficial‬ for sponsoring my trip to .Conf 2026 and also for sponsoring this video. AI agents can do things you never intended. So how do you monitor their behavior, spot security problems and decide what they should be allowed to do? I’m joined by Splunk’s Kamal Hathi at .conf26 to discuss AI agent security, observability and what an agentic SOC means for the people working in cybersecurity. Kamal explains why setting a goal isn’t enough. You need visibility into what your agents are actually doing, clear guardrails and human oversight for important decisions. We also discuss why monitoring only a sample of agent activity can leave gaps, and how focused small language models could help reduce evaluation costs. In this interview, we cover: • Known agents, unregistered agents and unexpected behavior • AI evaluations, guardrails and zero trust • Automating SOC alert triage while keeping humans in control • Using AI to create SOAR playbooks • Running models locally for privacy, cost and control • Choosing between local models and cloud models • Whether you should still study computer science in 2027 If you’re building AI agents, working in cybersecurity or deciding what to learn next, this conversation will give you plenty to think about. // Kamal Hathi’s’ SOCIAL // LinkedIn: / kamal-hathi // David's SOCIAL // Discord: discord.com/invite/usKSyzb Twitter: www.twitter.com/davidbombal Instagram: www.instagram.com/davidbombal LinkedIn: www.linkedin.com/in/davidbombal Facebook: www.facebook.com/davidbombal.co TikTok: tiktok.com/@davidbombal YouTube: / @davidbombal Spotify: open.spotify.com/show/3f6k6gE... SoundCloud: / davidbombal Apple Podcast: podcasts.apple.com/us/podcast... // MY STUFF // https://www.amazon.com/shop/davidbombal // SPONSORS // Interested in sponsoring my videos? Reach out to my team here: sponsors@davidbombal.com Please note that links listed may be affiliate links and provide me with a small percentage/kickback should you use them to purchase any of the items listed or recommended. Thank you for supporting me and this channel! Disclaimer: This video is for educational purposes only. #SplunkConf26 #Splunk #Cisco

  • October 1 · 22 min

    #610: WiFi Pineapple Pager: What Can It Actually Do?

    Big thank you to proton VPN for sponsoring the video. To get 70% off your Proton VPN subscription use the following link: https://protonvpn.com/davidbombal Note: Hak5 did not pay me to make this video. But, for full transparency: Darren was kind enough to give me some cool Hak5 gadgets. Get your own using my link below. // Buy Hak5 coolness here (Affiliate Link): // Buy Hak5: https://davidbombal.wiki/gethak5 WiFi hacking without opening your laptop? ‪@DarrenKitchen‬ from ‪@hak5‬ joins me to talk about the WiFi Pineapple Pager and what this little Linux device can actually do. Darren shares the story behind the Pager, explains its support for 2.4, 5, and 6 GHz WiFi, and walks us through features including wireless reconnaissance, eventtriggered alerts, and community-created payloads. We also discuss how Bash and DuckyScript helpers let users build their own functionality, and how Pager Portal makes it possible to download payloads directly onto the device. How does it compare with the WiFi Pineapple Mark VII and Enterprise? We look at the different use cases, from portable testing to remotely auditing a client’s wireless network. And yes, someone has already made it run Doom. This is an interview and feature overview with the creator, covering the ideas, technology, and community behind the WiFi Pineapple Pager. // Darren Kitchen SOCIAL // YouTube: / darrenkitchen Website: https://hak5.org/pages/hack-across-am... X: https://x.com/hak5darren // Hak5 WEBSITE // https://shop.hak5.org/ // Previous YouTube video with Darren REFERENCE // Hacking Gadgets Every Cybersecurity Pro should know: • Hacking Gadgets Every Cybersecurity Pro Sh... // David's SOCIAL // Discord: discord.com/invite/usKSyzb Twitter: www.twitter.com/davidbombal Instagram: www.instagram.com/davidbombal LinkedIn: www.linkedin.com/in/davidbombal Facebook: www.facebook.com/davidbombal.co TikTok: tiktok.com/@davidbombal YouTube: / @davidbombal Spotify: open.spotify.com/show/3f6k6gE... SoundCloud: / davidbombal Apple Podcast: podcasts.apple.com/us/podcast... // MY STUFF // https://www.amazon.com/shop/davidbombal // SPONSORS // Interested in sponsoring my videos? Reach out to my team here: sponsors@davidbombal.com Please note that links listed may be affiliate links and provide me with a small percentage/kickback should you use them to purchase any of the items listed or recommended. Thank you for supporting me and this channel! Disclaimer: This video is for educational purposes only. #wifipineapplepager #wifi #hackinggadgets

  • S1 · E1
    October 1 · 39 min

    #609: How Hackers Target Satellites Through Ground Control Systems

    Big thanks to DeleteMe for sponsoring this video. Protect your business with DeleteMe by using the following Link: https://joindeleteme.com/bombal-biz You’ll also get a free year of social media protection for every seat you purchase. How do you hack a satellite? The attack can start on the ground. Watch a mission control demo showing how web vulnerabilities can change a simulated spacecraft’s orbit. At DEF CON, I meet Milenko and Andrzej, the authors of The Spacecraft Hackers Handbook, to explore spacecraft cybersecurity. They explain the infrastructure behind satellite operations, what the Via sat attack actually targeted, and why protecting spacecraft requires both security and space engineering knowledge. Then Andrzej demonstrates previously patched vulnerabilities in an older version of mission control software. Using Burp Suite, he shows how path traversal exposes configuration files and how cross-site scripting can trigger a spacecraft command through an operator’s browser. We cover: • Why satellite security extends to systems on the ground • How path traversal and XSS affect mission control software • Telemetry, telecommands, CCSDS and the SDLS security layer • How GPS supports timing as well as navigation • Python examples, a prepared lab VM and learning resources • The authors’ nine satellite cybersecurity challenges on Hack The Box • Skills and career opportunities in spacecraft cybersecurity The demonstration uses a spacecraft simulator. The vulnerabilities shown were disclosed to the vendor and patched. // Link to No Starch Website for Milenko and Andrzej’s Book// The Spacecraft Hacker’s Handbook: https://nostarch.com/spacecraft-hacke... Use Coupon Code SPACE25 for 25% off The Spacecraft Hacker’s Handbook. // Milenko Starcik’s SOCIALS // Website: https://visionspace.com/team/milenko-... Website 2: https://starcik.space/ // Andrzej Olchawa’s SOCIALS // Website: https://visionspace.com/author/a-olch... Website 2: https://andy.codes/ X: https://x.com/0x4ndy // Online Resources // https://spacesecurity.club https://github.com/orgs/spacecrafthac... // Blog Post REFERENCE // https://www.hackthebox.com/blog/hack-... // David's SOCIAL // Discord: discord.com/invite/usKSyzb Twitter: www.twitter.com/davidbombal Instagram: www.instagram.com/davidbombal LinkedIn: www.linkedin.com/in/davidbombal Facebook: www.facebook.com/davidbombal.co TikTok: tiktok.com/@davidbombal YouTube: / @davidbombal Spotify: open.spotify.com/show/3f6k6gE... SoundCloud: / davidbombal Apple Podcast: podcasts.apple.com/us/podcast... // MY STUFF // https://www.amazon.com/shop/davidbombal // SPONSORS // Interested in sponsoring my videos? Reach out to my team here: sponsors@davidbombal.com Please note that links listed may be affiliate links and provide me with a small percentage/kickback should you use them to purchase any of the items listed or recommended. Thank you for supporting me and this channel! Disclaimer: This video is for educational purposes only. #sattelitehacking #spacecraftcybersecurity #defcon

  • S1 · E1
    September 19 · 52 min

    #608: Before You Deploy AI Agents, Understand These Attacks

    Big thanks to Proton VPN for sponsoring this video. You can use my link: https://protonvpn.com/davidbombal to get 70% off your Proton VPN subscription How do you hack an AI system? And what happens when one malicious instruction spreads between AI agents? I’m joined by Harriet, author of Practical AI Security, to explore how AI models and agents can be manipulated, with practical Python demonstrations. You'll see an image classifier misidentify a rifle, a demonstration of prompt injection spreading across five agents, and how memory poisoning can plant instructions that affect an agent later. We discuss why securing AI takes more than blocking prompt injection, how machine learning creates different security challenges, and what you need to understand before deploying agents in your organisation. Want to learn this yourself? Harriet explains how to get started with her collection of 30+ free Python notebooks, including examples you can explore in Google Colab. We also discuss the skills involved in AI security and how people from different backgrounds can contribute. Topics include: • Adversarial machine learning and image manipulation • Prompt injection and attacks spreading between agents • Memory poisoning and model backdoors • AI supply chain security • Learning AI security with Python • AI security careers, training and fundamentals // Link to No Starch Website for Harriet Farlow’s Book // Order Practical AI Security on No Starch: https://nostarch.com/practical-ai-sec... Use Coupon code FARLOW25 for 25% off Practical AI Security // HarrietHacks Labs REFERENCE // https://labs.harriethacks.com/ // Harriet Farlow’s AI Security Fundamentals Course REFERENCE // https://aisecurityfundamentals.com/ // Harriet Farlow’s SOCIALS // Website: https://harriethacks.com/about/ LinkedIn: / harriet-farlow-654963b7 Instagram: / harriethacks // David's SOCIAL // Discord: discord.com/invite/usKSyzb Twitter: www.twitter.com/davidbombal Instagram: www.instagram.com/davidbombal LinkedIn: www.linkedin.com/in/davidbombal Facebook: www.facebook.com/davidbombal.co TikTok: tiktok.com/@davidbombal YouTube: / @davidbombal Spotify: open.spotify.com/show/3f6k6gE... SoundCloud: / davidbombal Apple Podcast: podcasts.apple.com/us/podcast... // MY STUFF // https://www.amazon.com/shop/davidbombal // SPONSORS // Interested in sponsoring my videos? Reach out to my team here: sponsors@davidbombal.com // MENU // 0:00 - Intro 01:05 - Harriet Farlow AI security background 05:55 - Proton VPN sponsor segment 08:02 - Practical AI Security book // AI Security 10:40 - Who's the book for 11:32 - Harriet's YouTube channel 12:32 - AI security course 14:27 - Practical demos 15:41 - Hacking an AI demo // Learning how AIs work 22:22 - Hacking an AI summary 24:40 - Hacking an AI visualizations 28:48 - AI deceiving another AI 33:09 - Hacking an AI visualizations continued 34:07 - Rushing to the AI market 36:26 - Adversarial patch explained 38:12 - Vibe coded visuals 40:27 - More visualization 44:04 - Growth of interest in AI security 45:09 - No advanced skills required 49:40 - Get in contact with Harriet Farlow // Conclusion Please note that links listed may be affiliate links and provide me with a small percentage/kickback should you use them to purchase any of the items listed or recommended. Thank you for supporting me and this channel! Disclaimer: This video is for educational purposes only. #aisecurity #aiagents #defcon

  • S1 · E1
    September 19 · 31 min

    #607: How Hackers Steal Your Accounts Even With 2FA Enabled

    Big thanks to ThreatLocker for sponsoring my trip to Black Hat USA 2026 and also for sponsoring this video. To start your free trial with ThreatLocker please use the following link: https://www.threatlocker.com/davidbombal Is Microsoft Defender enough to protect your PC? Malware researcher Leo joins me at Black Hat to discuss antivirus, Windows security and how hackers steal your accounts. We explore how infostealers target saved passwords and session tokens, why two-factor authentication cannot prevent every account takeover, and how a message from a compromised friend’s account can lead to an infection. Leo shares practical starting points for investigating your computer, including Autoruns for startup entries, TCPView for linking connections to applications, and Wireshark for examining network traffic. We also discuss password managers, account recovery planning, Windows telemetry and why switching operating systems does not eliminate security risks. In this interview: • Microsoft Defender’s strengths and limitations • Free tools for investigating suspicious Windows activity • How infostealers and initial access brokers operate • Stolen session tokens and the limits of 2FA • Fake download sites, malicious ads and targeted phishing • Preparing recovery options before your accounts are compromised • Security and privacy trade-offs across Windows, Linux and macOS // Leo’s SOCIAL // YouTube: / @pcsecuritychannel X: https://x.com/leotday Discord: / discord // David's SOCIAL // Discord: discord.com/invite/usKSyzb Twitter: www.twitter.com/davidbombal Instagram: www.instagram.com/davidbombal LinkedIn: www.linkedin.com/in/davidbombal Facebook: www.facebook.com/davidbombal.co TikTok: tiktok.com/@davidbombal YouTube: / @davidbombal Spotify: open.spotify.com/show/3f6k6gE... SoundCloud: / davidbombal Apple Podcast: podcasts.apple.com/us/podcast... // MY STUFF // https://www.amazon.com/shop/davidbombal // SPONSORS // Interested in sponsoring my videos? Reach out to my team here: sponsors@davidbombal.com Please note that links listed may be affiliate links and provide me with a small percentage/kickback should you use them to purchase any of the items listed or recommended. Thank you for supporting me and this channel! #malware #bhusa2026 #microsoftdefender

  • S1 · E1
    September 19 · 31 min

    #606: Is Cybersecurity Still Worth Learning in 2026?

    Big thanks to ThreatLocker for sponsoring my trip to Black Hat USA 2026 and also for sponsoring this video. To start your free trial with ThreatLocker, please use the following link: https://www.threatlocker.com/davidbombal Is cybersecurity still worth learning in 2026? AI agents are changing vulnerability research, but where does that leave you? At Black Hat, I’m joined by Arizona State University professor Yan Shoshitaishvili to discuss what AI can actually do, where it falls short, and why he would still choose a career in cybersecurity today. Yan shares how his lab used AI agents and human-designed workflows to find what he describes as over 1,000 Linux kernel vulnerabilities triggerable by an unprivileged local user. Running 128 agents was only part of the story. Understanding which vulnerabilities to look for and improving the research process proved critical. We discuss: • How AI agents test potential vulnerabilities instead of simply reporting suspected bugs • How agentic AI compares with fuzzing and static analysis • Why finding new bugs does not automatically prove one tool is better • Why human expertise still matters in security research • How to use AI as a learning assistant without skipping the learning • Free, hands-on cybersecurity training through pwn.college • Yan’s advice for anyone considering cybersecurity in 2026 // Yan Shoshitaishvili SOCIAL // LinkedIn: / yan-shoshitaishvili-7024305 ASU website: https://www.asu.edu/ // ThreatLocker’s SOCIAL // LinkedIn: https://www.linkedin.com/company/thre... X: https://x.com/threatlocker Instagram: / threatlocker Website: https://www.threatlocker.com/ // David's SOCIAL // Discord: discord.com/invite/usKSyzb Twitter: www.twitter.com/davidbombal Instagram: www.instagram.com/davidbombal LinkedIn: www.linkedin.com/in/davidbombal Facebook: www.facebook.com/davidbombal.co TikTok: tiktok.com/@davidbombal YouTube: / @davidbombal Spotify: open.spotify.com/show/3f6k6gE... SoundCloud: / davidbombal Apple Podcast: podcasts.apple.com/us/podcast... // MY STUFF // https://www.amazon.com/shop/davidbombal // SPONSORS // Interested in sponsoring my videos? Reach out to my team here: sponsors@davidbombal.com Please note that links listed may be affiliate links and provide me with a small percentage/kickback should you use them to purchase any of the items listed or recommended. Thank you for supporting me and this channel! Disclaimer: This video is for educational purposes only. #aiagents #vulnerabilityresearch #bhusa2026

  • S1 · E1
    September 12 · 22 min

    #605: Flock Cameras: What They Can Reveal About Your Life

    Big thank you to DeleteMe for sponsoring this video. Use my link join https://joindeleteme.com/Bombal or use the QR code in the video to get 20% off. Your license plate could reveal more than you think. Flock cameras, vehicle tracking and OSINT can turn information about your car into clues about where you live and your daily routines. I’m joined by an OSINT expert to discuss how vehicle information can be connected with public records, why surveillance raises privacy concerns and what happens when people trust an incorrect license plate match. He shares his experiences of locating a missing car after a police search came up short and investigating a hit-and-run using a partial plate and publicly available information. We discuss: • Flock cameras and vehicle identification beyond license plates • How vehicle data can expose patterns in your movements • License plate recognition errors and the importance of verification • How public records can connect a vehicle to a person • The risks of surveillance access being abused • Privacy measures, their limitations and the need for accountability • DeFlock and community scrutiny of surveillance cameras How much can someone discover about you from the information you leave exposed? // Mishaal Kahn’s SOCIALS // LinkedIn: / mish-aal Website: https://www.mishaalkhan.com/ Tool created: https://www.operationprivacy.com/ // David's SOCIAL // Discord: discord.com/invite/usKSyzb Twitter: www.twitter.com/davidbombal Instagram: www.instagram.com/davidbombal LinkedIn: www.linkedin.com/in/davidbombal Facebook: www.facebook.com/davidbombal.co TikTok: tiktok.com/@davidbombal YouTube: / @davidbombal Spotify: open.spotify.com/show/3f6k6gE... SoundCloud: / davidbombal Apple Podcast: podcasts.apple.com/us/podcast... // MY STUFF // https://www.amazon.com/shop/davidbombal // SPONSORS // Interested in sponsoring my videos? Reach out to my team here: sponsors@davidbombal.com // MENU // 0:00 - Coming Up 0:47 - The Growing Flock Camera Controversy 01:28 - What Are Flock Cameras Actually Collecting? 02:33 - Police Misuse and Abuse of Surveillance Data 03:45 - Mapping and Avoiding Flock Cameras 04:57 - How Personal Data Fuels Scams 06:54 - What Can Police Actually Do With Flock Data? 07:12 - Testing Flock: A Real Missing Vehicle Case 09:09 - How Mishaal Found the Vehicle Himself 10:20 - Drones: The Next Level of Surveillance 11:11 - How Can You Protect Your Privacy? 13:07 - Facial Recognition Is Expanding Everywhere 14:13 - AI Can Rebuild Your Entire Pattern of Life 15:51 - What Can Someone Find From Your License Plate? 17:16 - Solving a Hit-and-Run With a Partial Plate 19:08 - What Could a Rogue Police Officer Do? 20:28 - Is There Any Hope for Privacy? 21:53 - Where to Learn More About Privacy and OSINT Please note that links listed may be affiliate links and provide me with a small percentage/kickback should you use them to purchase any of the items listed or recommended. Thank you for supporting me and this channel! Disclaimer: This video is for educational purposes only. #flockcameras #defcon #privacy

  • S1 · E1
    September 12 · 24 min

    #604: How He Infiltrated LockBit and Helped Get Them Indicted

    Big thanks to Proton Drive for sponsoring this video. You can use my link http://proton.me/drive/davidbombal to sign up for Proton Drive and get 40% discount. John DiMaggio created fake identities, profiled ransomware operators and spent approximately 18 months earning the trust of LockBit. In this interview, John explains how his investigation led to work with the FBI and the UK’s National Crime Agency, contributed to indictments and resulted in death threats against him. He also reveals how the work affected his mental health, relationships and everyday life. John shares the remarkable story of a young REvil hacker connected to the Kaseya ransomware attack and its $70 million ransom demand. He explains how ransomware operators are recruited, manipulated and sometimes controlled by intelligence agencies. You will also learn why stolen cryptocurrency is difficult to spend, how Bitcoin tracing and money-laundering mistakes expose cybercriminals and why technical hacking skills do not make someone good at hiding money. Finally, John warns aspiring researchers not to approach ransomware gangs without professional training and support. He discusses his new book, Owned, and how he plans to use his experience to help cybersecurity teams and business leaders prepare for ransomware attacks. // Link to No Starch Website for Jon DiMaggio’s Book // Order Owned on No Starch: https://nostarch.com/owned Use Coupon Code OWNED30 for 30% off Owned at NoStarch.com // Jon DiMaggio’s SOCIALS // Website: https://arkemcyber.com/ X: https://x.com/Jon__DiMaggio LinkedIn: / jondimaggio // David's SOCIAL // Discord: discord.com/invite/usKSyzb Twitter: www.twitter.com/davidbombal Instagram: www.instagram.com/davidbombal LinkedIn: www.linkedin.com/in/davidbombal Facebook: www.facebook.com/davidbombal.co TikTok: tiktok.com/@davidbombal YouTube: / @davidbombal Spotify: open.spotify.com/show/3f6k6gE... SoundCloud: / davidbombal Apple Podcast: podcasts.apple.com/us/podcast... // MY STUFF // https://www.amazon.com/shop/davidbombal // SPONSORS // Interested in sponsoring my videos? Reach out to my team here: sponsors@davidbombal.com // MENU // 0:00 - Coming Up 0:36 - Introduction 01:28 - Infiltrating the LockBit Ransomware Gang 03:45 - Working With the FBI & NCA 04:55 - Sponsor – Proton Drive 06:54 - Stories From the Ransomware Gang 07:35 - Befriending a Hacker 10:21 - The Kaseya Ransomware Attack 12:10 - Arrest, Extradition & a 14-Year Sentence 13:12 - An Unexpected Message From Prison 14:57 - The LockBit Story & the Mental Health Toll 16:30 - Advice for Young People Drawn to Cybercrime 18:09 - Why Hackers Can’t Easily Spend Their Money 19:12 - How to Become a Jon DiMaggio 21:58 - What’s Next for Jon DiMaggio 23:08 - Preparing Companies for Ransomware Attacks 23:52 - Final Thoughts Please note that links listed may be affiliate links and provide me with a small percentage/kickback should you use them to purchase any of the items listed or recommended. Thank you for supporting me and this channel! Disclaimer: This video is for educational purposes only. #lockbit #ransomware #revil

  • S1 · E1
    September 8 · 47 min

    #603: How Age Verification Threatens Your Online Privacy

    Big thanks to ThreatLocker for sponsoring my trip to Black Hat USA 2026 and also for sponsoring this video. To start your free trial with ThreatLocker please use the following link: www.threatlocker.com/davidbombal Age verification is spreading across the internet. It promises to protect children, but what happens when accessing a website or using your own device requires facial recognition, identity documents or third-party verification? David speaks with Alexis Hancock from the Electronic Frontier Foundation about the growing privacy risks surrounding age verification and digital ID systems. They examine how these technologies could threaten online anonymity, create new surveillance infrastructure and expose sensitive personal information. Alexis explains why age verification alone does not teach children how to stay safe online, how data brokers and behavioral advertising contribute to the problem, and why banning VPNs or weakening encryption would make everyone less secure. They also discuss zero-knowledge proofs, facial recognition, encryption backdoors, government surveillance and the danger of building a digital identity system that could be abused by future governments. Finally, Alexis shares practical ways to protect your privacy, including using encrypted communication, learning from EFF’s Surveillance Self-Defense guides and contacting elected representatives when harmful legislation is proposed. // Alexis Hancock’ SOCIAL // LinkedIn: / alexishancock // EFF Website REFERENCE // www.eff.org/ // David's SOCIAL // Discord: discord.com/invite/usKSyzb Twitter: www.twitter.com/davidbombal Instagram: www.instagram.com/davidbombal LinkedIn: www.linkedin.com/in/davidbombal Facebook: www.facebook.com/davidbombal.co TikTok: tiktok.com/@davidbombal YouTube: / @davidbombal Spotify: open.spotify.com/show/3f6k6gE... SoundCloud: / davidbombal Apple Podcast: podcasts.apple.com/us/podcast... // MY STUFF // www.amazon.com/shop/davidbombal // SPONSORS // Interested in sponsoring my videos? Reach out to my team here: sponsors@davidbombal.com // MENU // 0:00 - Intro 0:41 - Alexis Hancock background // Who are the EFF 01:48 - Eroding privacy & age verification 08:48 - Online safety for children 12:25 - Online monitoring 14:20 - ThreatLocker sponsor segment 15:27 - Big tech vs government 17:49 - How to fight for privacy 20:19 - Online censorship & privacy 26:17 - The push for age verification 29:29 - Age verification "whack-a-mole" 33:03 - Parental control vs age verification 36:24 - What about non-tech savvy people? 41:02 - Zero-knowledge proof 44:48 - Is it too late? // Conclusion Please note that links listed may be affiliate links and provide me with a small percentage/kickback should you use them to purchase any of the items listed or recommended. Thank you for supporting me and this channel! Disclaimer: This video is for educational purposes only. #ageverification #privacy #bhusa2026

  • S1 · E1
    September 8 · 30 min

    #602: How Compilers Turn Secure C Code Into Vulnerable Binaries

    Big thanks to ‪@ThreatLocker‬ for sponsoring my trip to Black Hat USA 2026 and also for sponsoring this video. To start your free trial with ThreatLocker please use the following link: https://www.threatlocker.com/davidbombal You can write secure C code, follow accepted best practices and still end up with a vulnerable binary. The reason is simple: the CPU does not run your source code. It runs whatever the compiler produces. David sits down with security researcher Chris Domas at Black Hat to examine how legal compiler optimizations can remove security protections, delete memory-clearing operations and introduce time-of-check to time-of-use vulnerabilities into code that appeared secure. Chris explains the C abstract machine, why compilers are allowed to transform code so dramatically and how register pressure, structure layout and even data size can affect whether a binary is vulnerable. In one striking example, 17 or 33 bytes can be safe while nearby sizes produce vulnerable code. They also discuss whether Rust solves the problem, why switching between GCC and Clang is not the answer and how AI helped analyse 500 million lines of open-source code to identify 300 potentially dangerous patterns. Most importantly, Chris explains what developers can do now, including enabling compiler warnings, using sanitizers, analysing optimized builds and testing the exact binary that will be shipped. // Christopher Domas’ SOCIAL // LinkedIn: / christopher-domas GitHub: https://github.com/xoreaxeaxeax X: https://x.com/xoreaxeaxeax // David's SOCIAL // Discord: discord.com/invite/usKSyzb Twitter: www.twitter.com/davidbombal Instagram: www.instagram.com/davidbombal LinkedIn: www.linkedin.com/in/davidbombal Facebook: www.facebook.com/davidbombal.co TikTok: tiktok.com/@davidbombal YouTube: / @davidbombal Spotify: open.spotify.com/show/3f6k6gE... SoundCloud: / davidbombal Apple Podcast: podcasts.apple.com/us/podcast... // MY STUFF // https://www.amazon.com/shop/davidbombal // SPONSORS // Interested in sponsoring my videos? Reach out to my team here: sponsors@davidbombal.com Please note that links listed may be affiliate links and provide me with a small percentage/kickback should you use them to purchase any of the items listed or recommended. Thank you for supporting me and this channel! Disclaimer: This video is for educational purposes only. #bhusa2026 #securecoding #compiler

  • S1 · E1
    September 8 · 39 min

    #601: Google Researchers Hacked the Pixel Phone using Audio Messages

    Big thanks to ThreatLocker for sponsoring my trip to Black Hat USA 2026 and also for sponsoring this video. To start your free trial with ThreatLocker please use the following link: https://www.threatlocker.com/davidbombal A zero-click attack can compromise your phone without you opening a link, installing an application or even touching the device. David sits down with Natalie Silvanovich and Seth Jenkins from Google Project Zero to examine how specially crafted audio messages were used to remotely compromise the Pixel 9 and Pixel 10. The attack begins inside the Dolby Unified Decoder, where Android automatically processes incoming audio for transcription. The researchers explain how they exploited the decoder, escaped the media codec sandbox and targeted vulnerable Pixel hardware drivers to achieve kernel code execution and root access. They also discuss ASLR, SELinux, memory corruption, the eight-week exploit development process, how AI helped automate repetitive tasks and why Apple’s compiler protections prevented the same Dolby bug from affecting iPhones. Most importantly, they explain what manufacturers can do to reduce their attack surface and make commercial zero-click exploits significantly more expensive. These vulnerabilities were responsibly disclosed and patched. Pixel users running the latest security updates are protected. // Seth Jenkins SOCIAL // LinkedIn: https://www.linkedin.com/in/seth-jenkins-a20b914b/ X: https://x.com/__sethJenkins // Natalie Silvanovich SOCIAL // X: https://x.com/natashenka?lang=en Website: https://natashenka.ca/ // Website REFERENCE // Google Project Zero website: https://projectzero.google/ // David's SOCIAL // Discord: discord.com/invite/usKSyzb Twitter: www.twitter.com/davidbombal Instagram: www.instagram.com/davidbombal LinkedIn: www.linkedin.com/in/davidbombal Facebook: www.facebook.com/davidbombal.co TikTok: tiktok.com/@davidbombal YouTube: / @davidbombal Spotify: open.spotify.com/show/3f6k6gE... SoundCloud: / davidbombal Apple Podcast: podcasts.apple.com/us/podcast... // MY STUFF // https://www.amazon.com/shop/davidbombal // SPONSORS // Interested in sponsoring my videos? Reach out to my team here: sponsors@davidbombal.com // MENU// 0:00 - Intro 01:00 - ThreatLocker sponsor segment 02:10 - Natalie Silvanovich background 04:00 - Seth Jenkins background 04:49 - Zero click audio codec vulnerability 05:41 - Disclaimer 06:07 - Hacking using audio files // How it works 10:23 - What happens in the sandbox 13:27 - The next step 15:15 - Running into issues 22:55 - Would someone notice the hack? 26:20 - Not secure by default 27:44 - Using AI assistance 29:44 - How to reduce attack surface 34:57 - How to get into cybersecurity 39:05 - Conclusion Please note that links listed may be affiliate links and provide me with a small percentage/kickback should you use them to purchase any of the items listed or recommended. Thank you for supporting me and this channel! Disclaimer: This video is for educational purposes only. #google #bhusa2026 #pixel10

Showing 1–20 of 42 episodes