Welcome to CyberCode Academy — your audio classroom for Programming and Cybersecurity. 🎧 Each course is divided into a series of short, focused episodes that take you from beginner to advanced level — one lesson at a time. From Python and web development to ethical hacking and digital defense, our content transforms complex concepts into simple, engaging audio learning. Study anywhere, anytime — and level up your skills with CyberCode Academy. 🚀 Learn. Code. Secure.
This episode, we shift our focus from application development to the security of the underlying server infrastructure.A newly deployed server can quickly become a target for automated scanning, credential attacks, and other unauthorized activity....
This final hands-on integration session, we bring the client-side component and the central control panel together into a complete communication workflow.The episode focuses on transforming an isolated client application into an integrated node...
This episode, we bring the control-panel backend together into a complete PHP, MySQL, and JavaScript database-driven communication architecture.Building on the authentication and dashboard functionality from previous episodes, we now connect the...
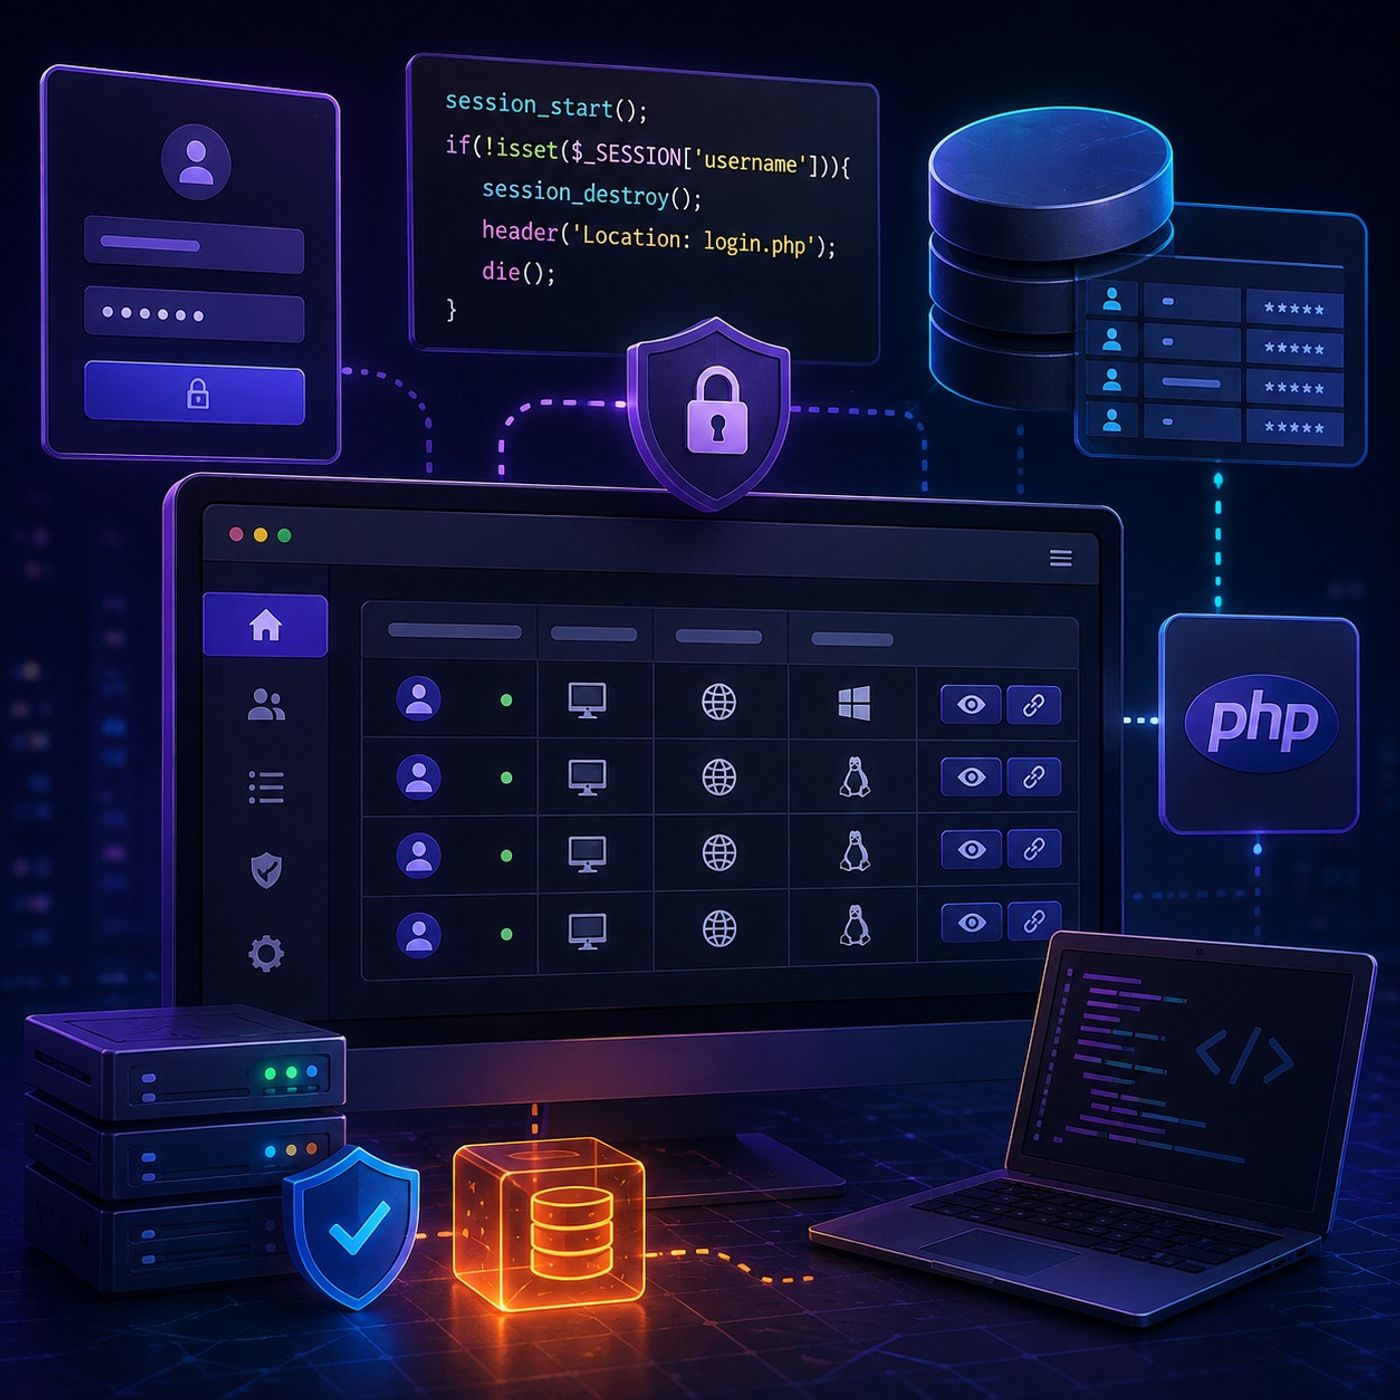
This episode, we continue developing our PHP-based control panel by moving beyond authentication and building the authenticated administration layer.We begin by establishing administrator credentials, then implement a dedicated session-protection...
This episode, we build a PHP and MySQL control panel backend from the ground up, progressing from database initialization and server configuration to user authentication and session management.The episode focuses on connecting a web application to a...
This episode moves beyond local command processing and introduces the fundamentals of network-based communication in a C# security-testing environment.The lesson begins by improving the reliability of the existing application through structured...
In this episode, we build a custom interactive command-line shell in C#, exploring how applications can combine filesystem navigation, system reconnaissance, and operating-system command execution into a single interface.The episode takes a practical,...
This episode introduces the core concepts behind offensive C# development for authorized penetration testing and red-team environments. The walkthrough follows a simplified offensive-tool lifecycle, beginning with host reconnaissance and progressing...
This episode establishes the essential development foundations across Windows and Linux, preparing the workspace for advanced scripting, application development, and future security-focused projects.The episode takes a practical, hands-on approach,...
This episode provides a complete, step-by-step guide to building a practical virtual sandbox using VirtualBox or VMware. The goal is to create isolated and reliable Windows and Linux environments that can be used for software development, testing, and...
This module provides a hands-on exploration of mobile malware analysis through two distinct case studies, one for iOS and one for Android, designed to let you work independently to uncover the functionality of malicious programs. The episode is...
This episode provides a comprehensive guide to designing and equipping a professional mobile malware analysis lab, with a focus on building a secure, repeatable, and well-instrumented environment for both iOS and Android research.1. Lab Design and...
This episode focuses on designing a professional, scalable, and repeatable mobile malware analysis laboratory, moving beyond a simple virtual-machine setup toward an environment suitable for long-term security research.1. Strategic Lab PlanningBefore...
This episode covers dynamic analysis of Android applications, with a strong emphasis on runtime interaction, monitoring, and debugging.1. Android Dynamic Analysis with DrozerThe episode introduces Drozer, an Android security assessment framework that...
Dynamic Mobile Malware Analysis — iOS and AndroidThis episode expands dynamic malware analysis beyond basic runtime observation and introduces process instrumentation, debugging, network capture, and automated mobile-security frameworks across both...
Dynamic iOS Malware Analysis — Key Takeaways
- Application Entry Point
- The standard entry point for an iOS application is UIApplicationMain.
- It initializes the application runtime and connects the application to its App Delegate, which...
Mobile Malware Static Analysis — Module ConclusionThis episode serves as a knowledge check and consolidation of the basic static-analysis methodology covered across both iOS and Android. The emphasis is not on learning one particular tool, but on...
Android Basic Static Analysis — Advanced Study GuideThis episode demonstrates how to perform basic static analysis of Android applications, moving from initial malware triage to manifest analysis, code decompilation, and identification of suspicious...
iOS Basic Static Analysis — Advanced Study GuideThis episode moves from the fundamentals of iOS malware analysis into hands-on static binary analysis, demonstrating how command-line utilities and reverse-engineering tools can reveal valuable...
iOS Malware Analysis — Key TakeawaysThis episode introduces the fundamentals of iOS malware analysis, combining the historical evolution of mobile threats with the methodology used by security researchers to investigate them.1. Understanding Mobile...